Why Inner Gallery Works Without a Server
Inner Gallery has no backend and no accounts. Photos are encrypted on-device with optional E2E iCloud sync. Why that's a deliberate architecture choice and what it means for privacy.
- Inner Gallery has no backend and no accounts. Photos are encrypted on-device with CryptoKit and stored locally.
- Optional end-to-end encrypted iCloud sync runs through your own iCloud account.
- Jungle Labs never holds your decryption keys, and there is no PIN recovery.
- With no server to pay for, the app is sold as one-time purchases, with no subscription.
What a server does in a typical vault app
| Function | Role of the server |
|---|---|
| Account management | Credentials, login, password recovery |
| Photo storage | Photos uploaded to the company's cloud |
| Payments | Subscriptions, receipts, entitlement checks |
| Analytics | Usage tracking, behavioral data, crash reports |
| Sync | Cross-device access to your photos |
Each of these creates a dependency and a potential point of failure or exploitation.
The problem with each server function
Accounts and password recovery
If an app offers "forgot your password," someone (the company, their server, a support agent) can reset your credentials and access your data. End-to-end encryption is incompatible with password recovery: the key must be derived from something only the user knows.
Cloud storage
Every server storing user data is a target. Data breaches in 2024 affected billions of records across industries, and a vault app gathers millions of private photos in one place.
The company can also access your photos unless it uses end-to-end encryption where it doesn't hold the keys. Most vault apps don't, as documented in Are Photo Vault Apps Actually Safe?.
Analytics
Analytics SDKs (Amplitude, Firebase, Facebook) collect screen views, session duration, feature usage, and device information. Even without touching your photos, they build a profile of your behavior inside a "privacy" app.
Keepsafe is a public example: Amplitude tracks 6 billion events there, and behavioral data is used to optimize pricing.
Recurring costs and subscriptions
Hosting, bandwidth, storage, and maintenance are paid every month. A $9.99/month subscription also funds the servers that store your photos.
This dynamic is covered in Why Vault Apps Charge Subscriptions.
How Inner Gallery works without a server
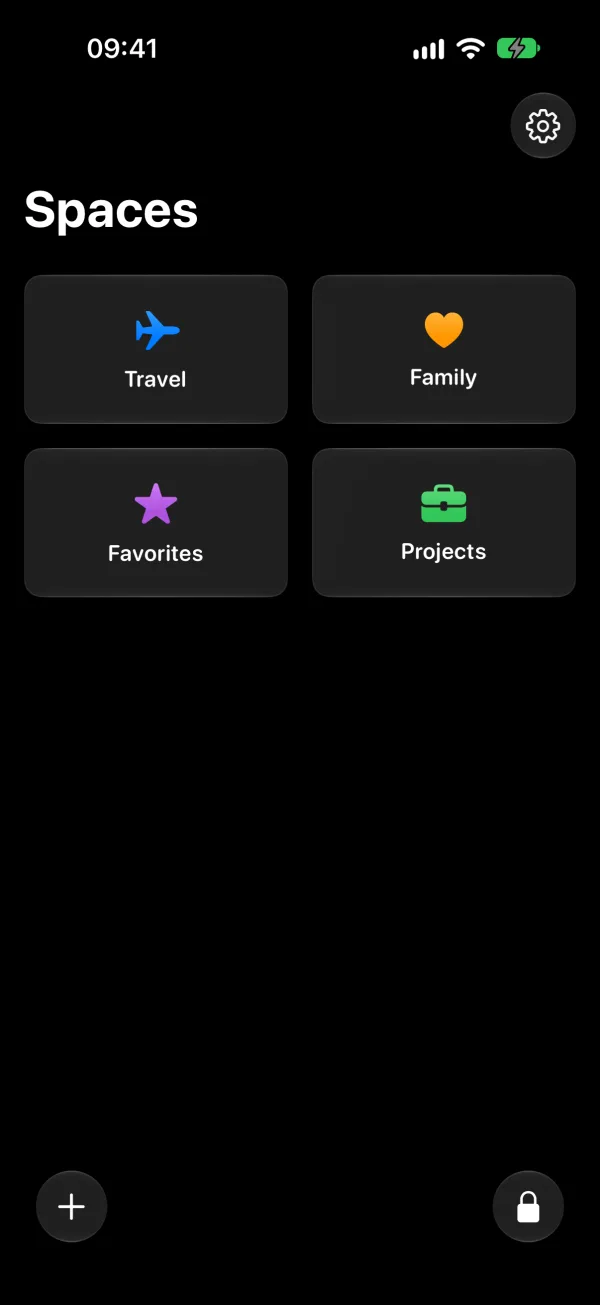
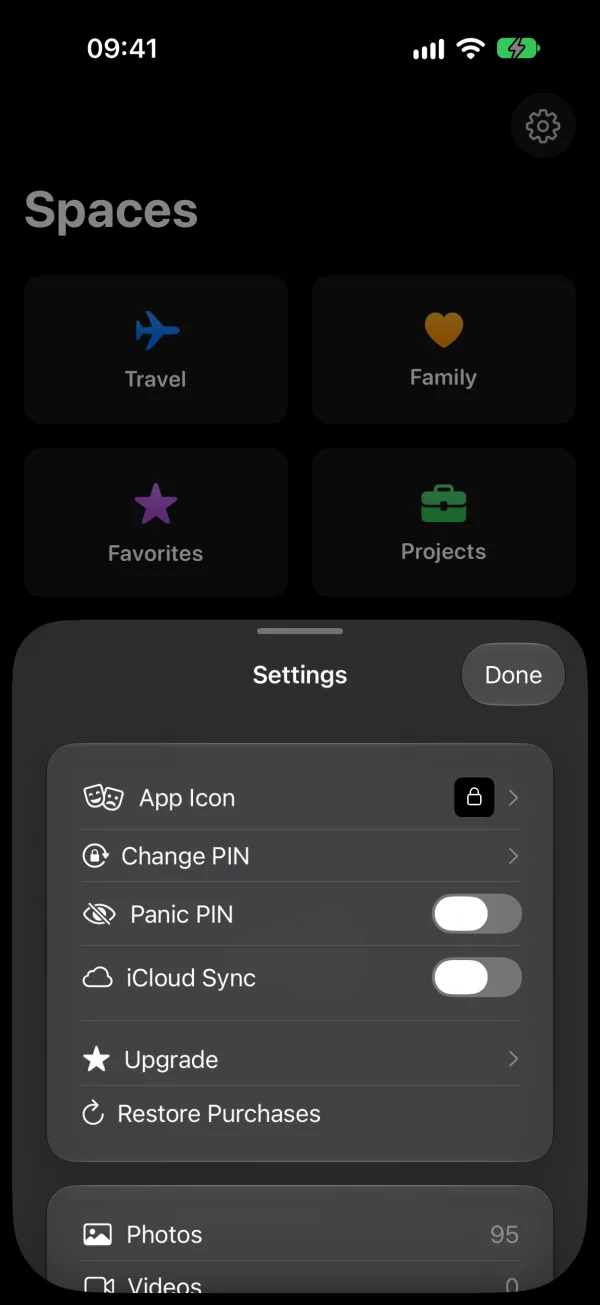
If the company can't recover your PIN, the company can't access your data.
The only network activity is optional iCloud sync: initiated by the user, end-to-end encrypted, and routed through the user's own iCloud account. The developers don't know which features are used most.
No recurring costs, no subscription
With no company servers to run, Inner Gallery uses a one-time purchase model. Once purchased, the features work forever.
| Tier | Price |
|---|---|
| Free tier (2 spaces, 50 items) | Free |
| Space Pack | €9.99 |
| Media Pack | €9.99 |
| Panic PIN | €9.99 |
| Cloud Sync | €14.99 |
| App Icons | €4.99 |
| Pro Bundle | €34.99 |
| Lifetime | €99.99 |
What about backups?
Without Cloud Sync, there are two backup strategies:
- iTunes/Finder encrypted backup: a full device backup includes the app's sandbox data, under the backup's encryption layer.
- iCloud device backup: if enabled, the app's data may be included in the device backup, encrypted with iCloud keys, or end-to-end with Advanced Data Protection.
Cloud Sync, end-to-end encrypted iCloud sync
Cloud Sync is an optional paid add-on (€14.99).
Jungle Labs has no server in the middle and no access to the data. Your iCloud stores only encrypted data it cannot read. The architecture stays zero-knowledge.
Panic spaces are never synced, by design. They exist only on the device where they were created.
The architecture in practice
| Feature | Server-based vault | Inner Gallery |
|---|---|---|
| Works offline | Sometimes | Always |
| Works without internet | Rarely | Always |
| Account required | Yes | No |
| Password recovery | Yes (server holds key) | No (by design) |
| Server-side data breach | Possible | No server to breach |
| Photos accessible to developer | Usually | Never |
| Subscription required | Usually | No |
| Analytics/tracking | Usually | None |
Why this matters for the encryption discussion
As explained in Photo Encryption on iPhone: What It Actually Means, the central question in encryption is who holds the key.
In a server-based vault, the key is often held by both the user and the company. In Inner Gallery, it is held by the user alone.
There is no server to send the key to, no account system to store it, no recovery mechanism that could expose it. The developers can't know what's in the app.
Related reading:
- How to Hide Photos on iPhone: every method compared, from Hidden album to encrypted vaults
- 5 Best Photo Vault Apps for iPhone: review of the top vault apps
- Photo Encryption Explained: what encrypted storage means for your photos
- Are Photo Vault Apps Actually Safe?: what most vault apps don't tell you